Continuous external attack surface management
Start with your domains. We'll find everything else.
TLDRecon maps your external attack surface and alerts you only when it matters.
- Built in Finland
- Hosted in the EU
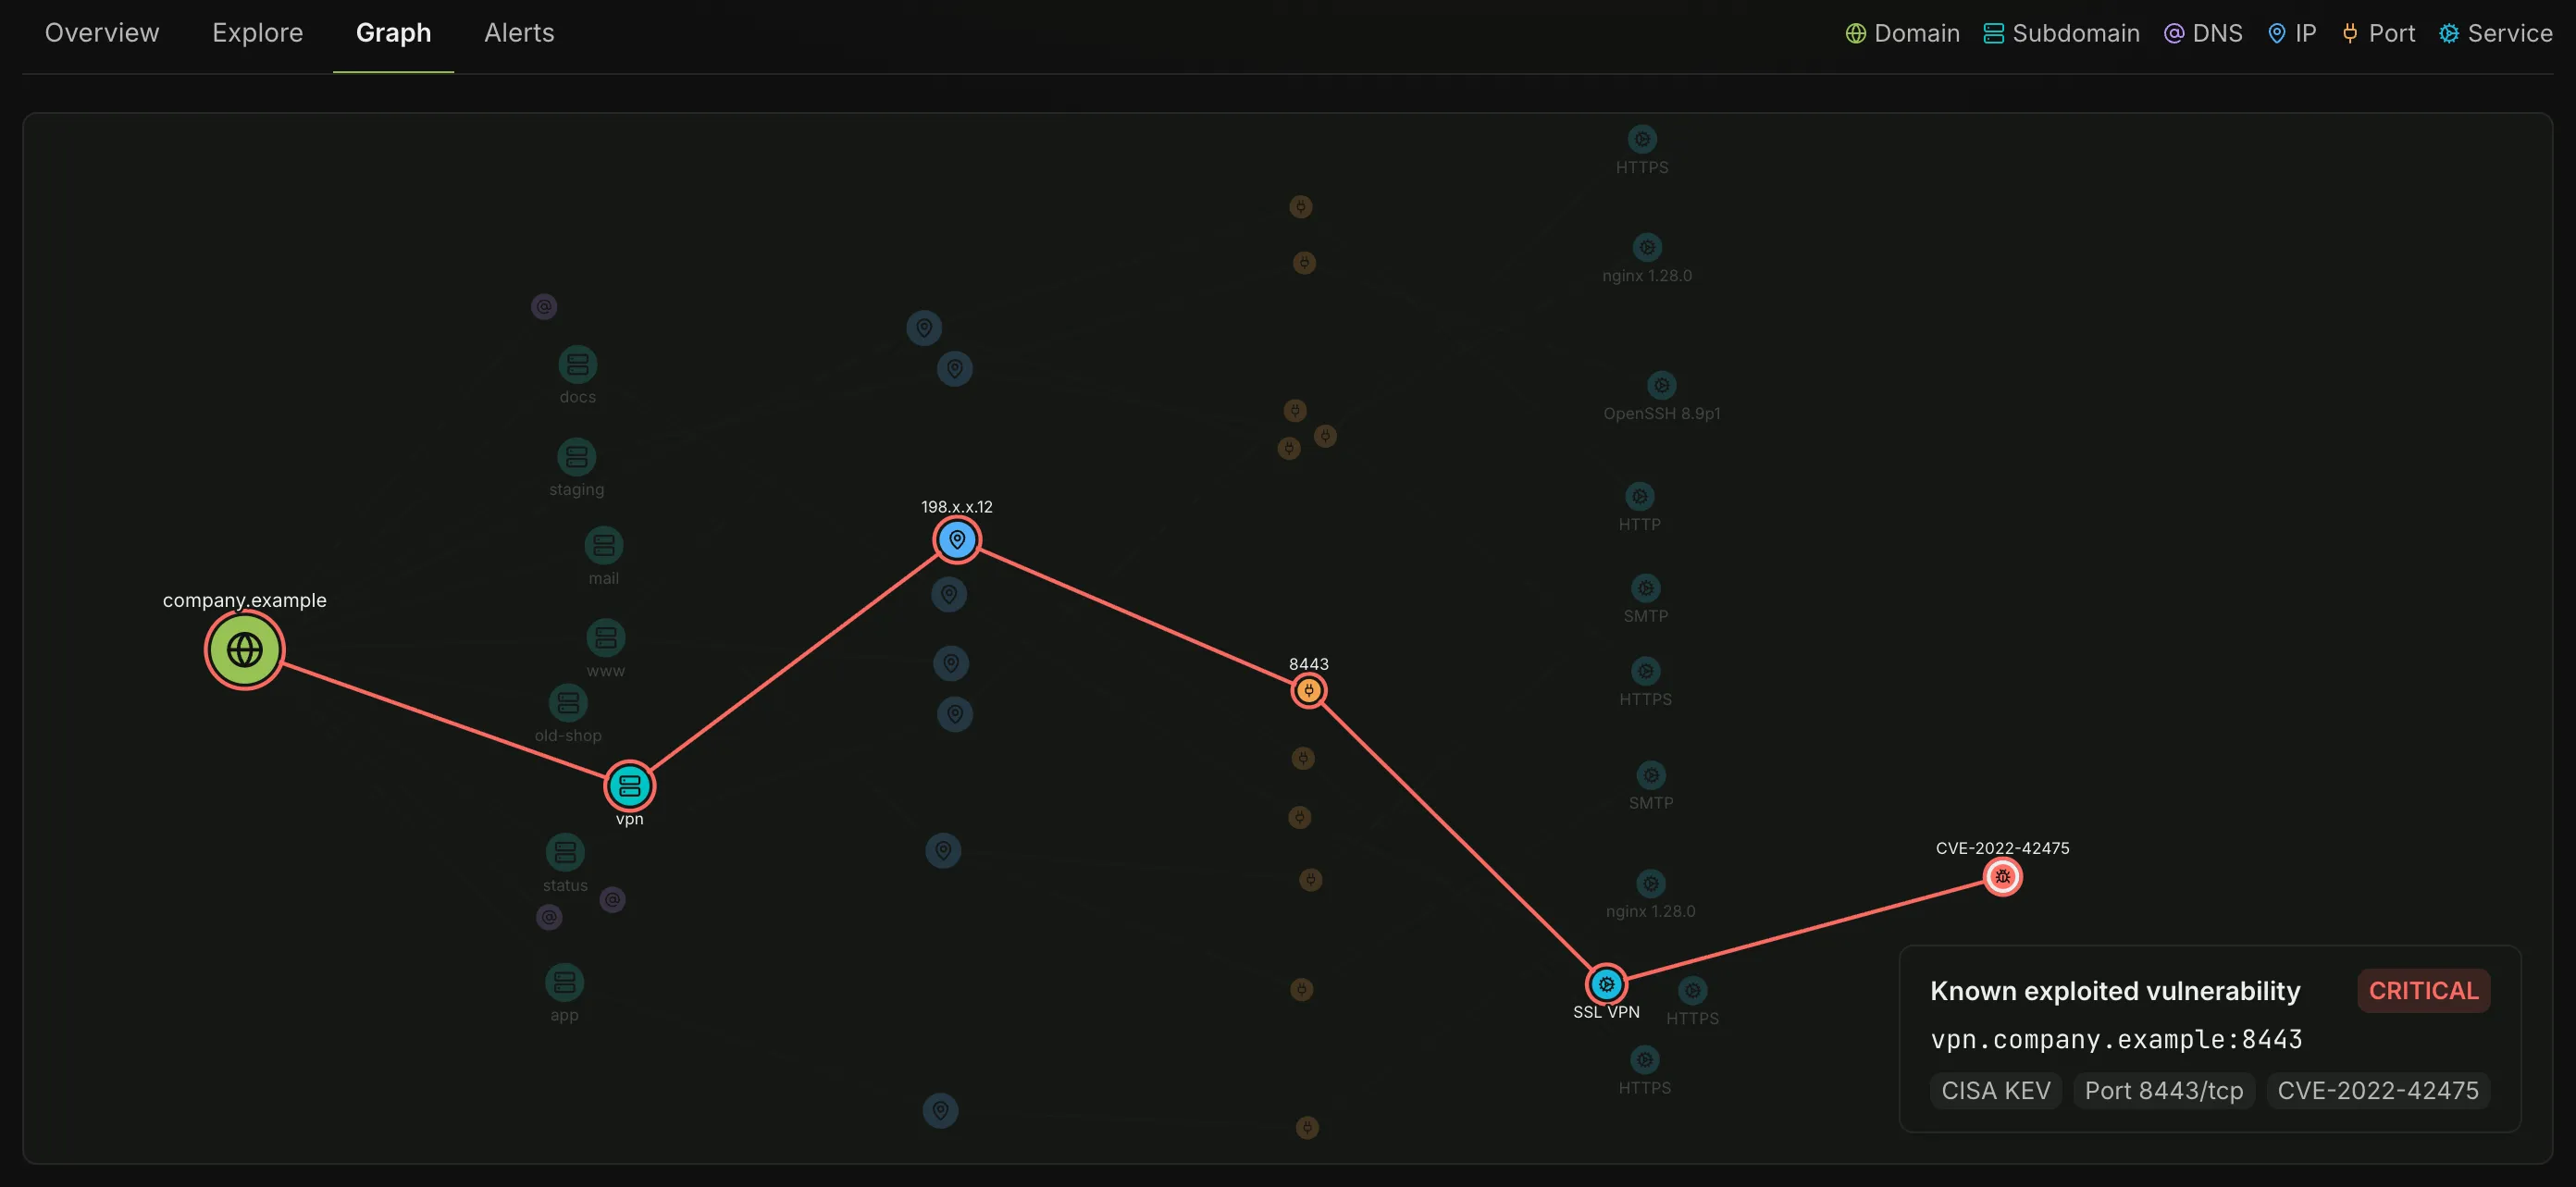
Your external attack surface, mapped and monitored
See everything you expose, from your own domains to your suppliers', and get alerted when something changes.
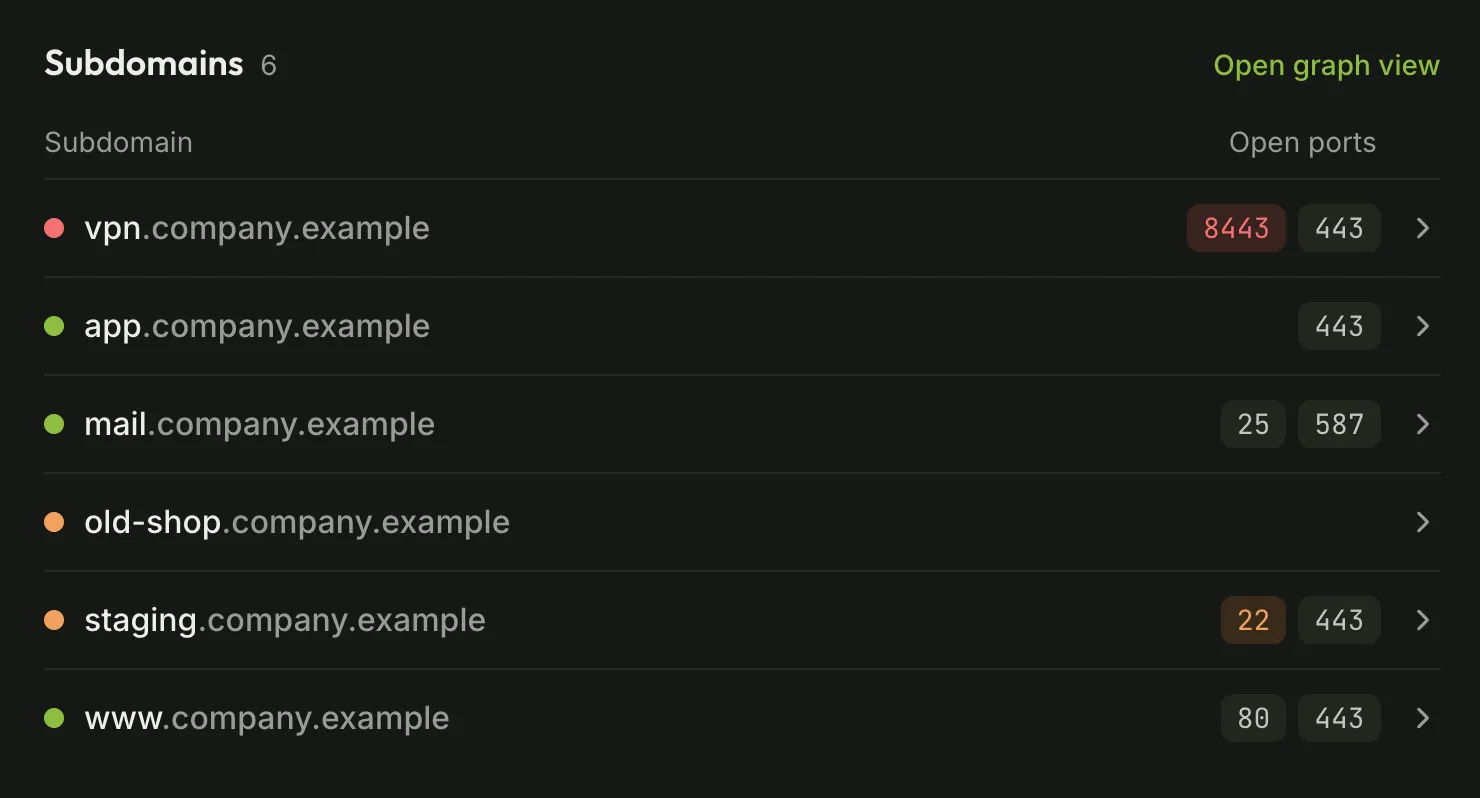
Continuous attack surface discovery
Add your domains and TLDRecon maps the rest of your external attack surface: related domains, subdomains and IP ranges. Connect your cloud providers with read-only access, and new public IPs and DNS zones are added to monitoring automatically.
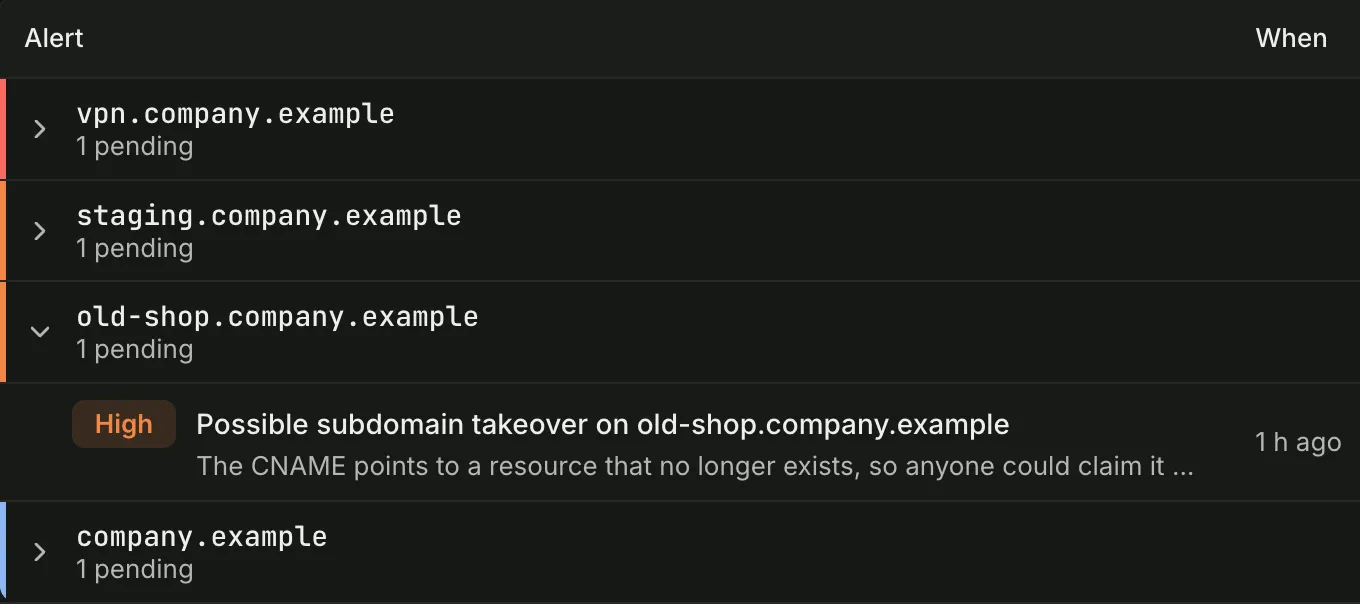
Exposure and vulnerability prioritization
Detect open ports, exposed admin panels, databases and end-of-life software. Every finding is scored with CVSS, CISA KEV and EPSS, so you focus on what attackers actually exploit.
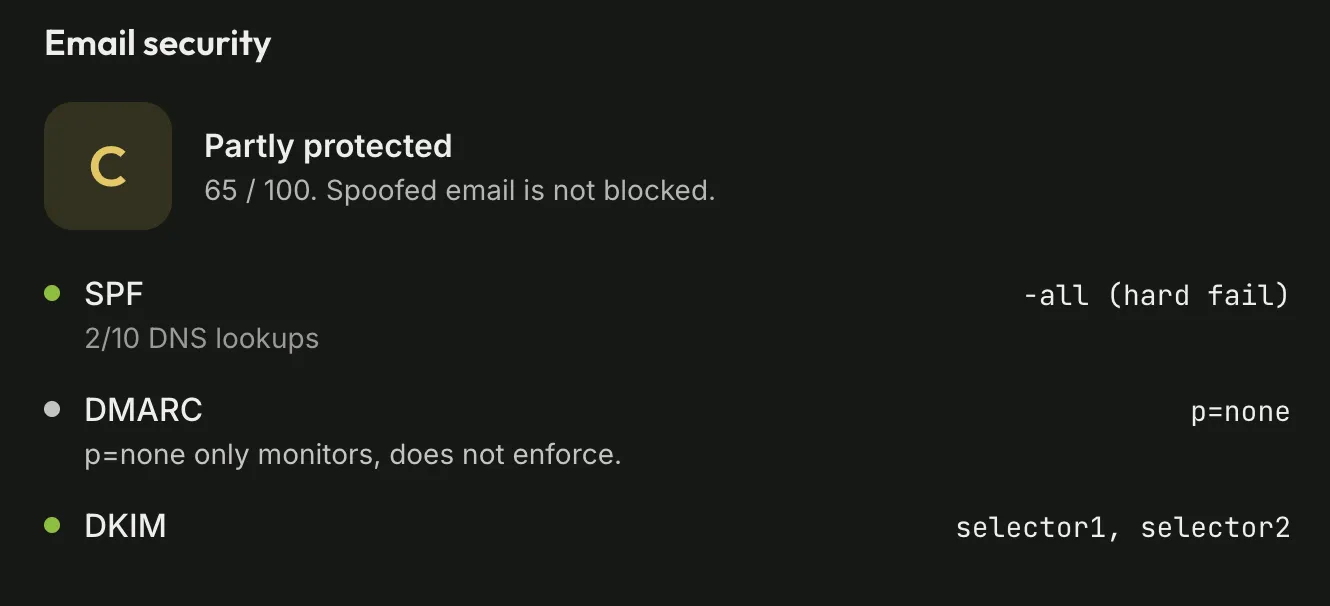
Domain and email security
Detect subdomain takeovers, SPF, DKIM and DMARC gaps, DNS misconfigurations and secrets leaked in DNS records. Get alerted to DNS changes, domain transfers and expiring domains and certificates.
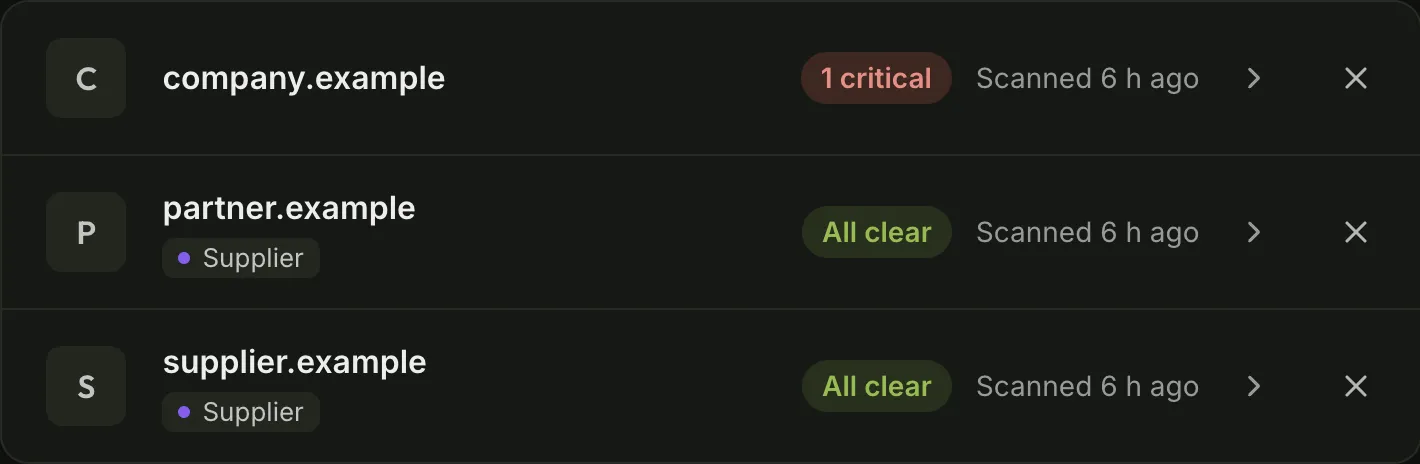
Supply chain risk monitoring
Monitor your suppliers' and partners' domains with the same alerts as your own. Know when a partner becomes a risk before it becomes your problem, and support your NIS2 supply chain requirements.
Works with the tools you already use
Your domains are all you need. Connect your cloud for automatic discovery.
Sync from
- AWS
- Microsoft Azure
- Google Cloud
- Cloudflare
Alert to
- Slack
- Microsoft Teams
- Webhook
How attack surface monitoring works
- 1
Add your domains
Your domains are all TLDRecon needs to get started. No agents, no installation. Optionally connect your cloud providers with read-only access.
- 2
TLDRecon maps your attack surface
Related domains, subdomains and IP ranges are discovered and scanned for exposures, vulnerabilities and misconfigurations, continuously. First results within an hour.
- 3
Get alerted when it matters
Findings are prioritized by real-world exploitation. Critical issues reach you instantly by email, Slack, Teams or webhook. Everything else arrives in a daily or weekly summary, grouped by root cause.
Frequently asked questions
What do I need to get started?
Just your domains. There are no agents to deploy and nothing to install. TLDRecon discovers the rest of your external attack surface from there.
Do I need to give TLDRecon access to my cloud environment?
No, it's optional. If you connect your cloud providers with read-only access, new public IPs and DNS zones are added to monitoring automatically.
How will I be alerted?
Critical issues reach you instantly by email, Slack, Teams or webhook. Everything else arrives in a daily or weekly summary, grouped by root cause.
Can I monitor my suppliers and partners?
Yes. You can monitor your suppliers' and partners' domains with the same alerts as your own, which also supports your NIS2 supply chain requirements.
What does the pilot program include?
Full access to TLDRecon, onboarding with our team, and direct feedback channels. There's no cost during the pilot.
What happens after the pilot?
You can continue on a paid subscription. There's no automatic billing and no obligation to continue.
Become a TLDRecon pilot customer
We're onboarding a limited number of organisations ahead of general availability in 2027. Pilot customers get full access free of charge, a direct line to the team building the product, and a real say in what we build next.